Personal Injury Law · Chino, CA
A Secure Rebuild After a Hack for a Personal Injury Law Firm in Chino, CA
MW Law Firm had their entire website hacked and taken down. They came looking for industry-level security experience, and the rebuild was designed so there is nothing sensitive on the site to take.
About the Client
MW Law Firm is a personal injury practice serving Chino and the surrounding Inland Empire. Their entire website was hacked and taken down, and they reached out for a web developer with industry-level security experience who could secure SSL and make sure no sensitive data would ever be present on the website.
The Challenge
Losing a website is bad for any business. For a law firm it is worse: the site is where injured people go to decide whether to trust you with the worst week of their life, and it went dark. The firm was not looking for a prettier page. They were looking for someone who could tell them, in specifics, why it would not happen again.
Their two requirements were concrete. SSL had to be handled properly and verifiably. And no sensitive information could live on the website at all, which rules out the plugin-and-database setup most law firm sites are built on.
What I Built
The site is hand-coded and static. There is no content management backend to compromise, no plugin ecosystem inheriting somebody else's vulnerabilities, and no stored client information sitting behind the pages waiting to be taken. SSL is enforced across the whole domain rather than bolted onto a single login page.
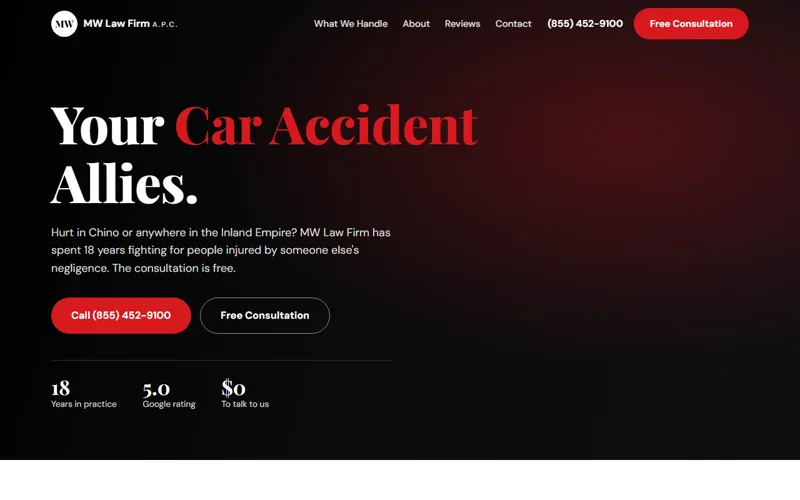
On top of that foundation, the page does the job a personal injury firm needs it to do. The hero states what the firm handles and who it is for, the phone number and the free consultation sit above the fold and repeat down the page, and the whole layout is built mobile-first for someone reading it one-handed from a hospital waiting room.
Under the Hood: Security By Having Nothing To Steal
The most reliable way to guarantee that sensitive data is never exposed on a website is to never put it there. Every page is compiled to plain HTML ahead of time and served as a static file over enforced SSL. There is no live database behind a request, no admin login exposed to the open internet, and no third-party plugin code executing on the server. The attack surface that took the old site down does not exist on this one.
Intake still works. A prospective client is pushed toward a phone call and a free consultation, which is where a personal injury conversation belongs anyway, instead of typing the details of their case into a form that then has to be stored and defended somewhere.
Project Gallery
The Results
- A firm that had been hacked and taken down is back online on a rebuilt foundation
- SSL enforced across the domain, as the firm specifically asked for
- No sensitive data present on the website at all, so there is nothing on it worth breaching
- A free consultation and a phone call reachable from the first screen and repeated down the page
Been hacked, or worried you will be?
I build professional-services sites with no database to breach and no plugins to patch.